Let's Encrypt Reduces Certificates to 64 Days: Why Should Website Owners Learn Automation?
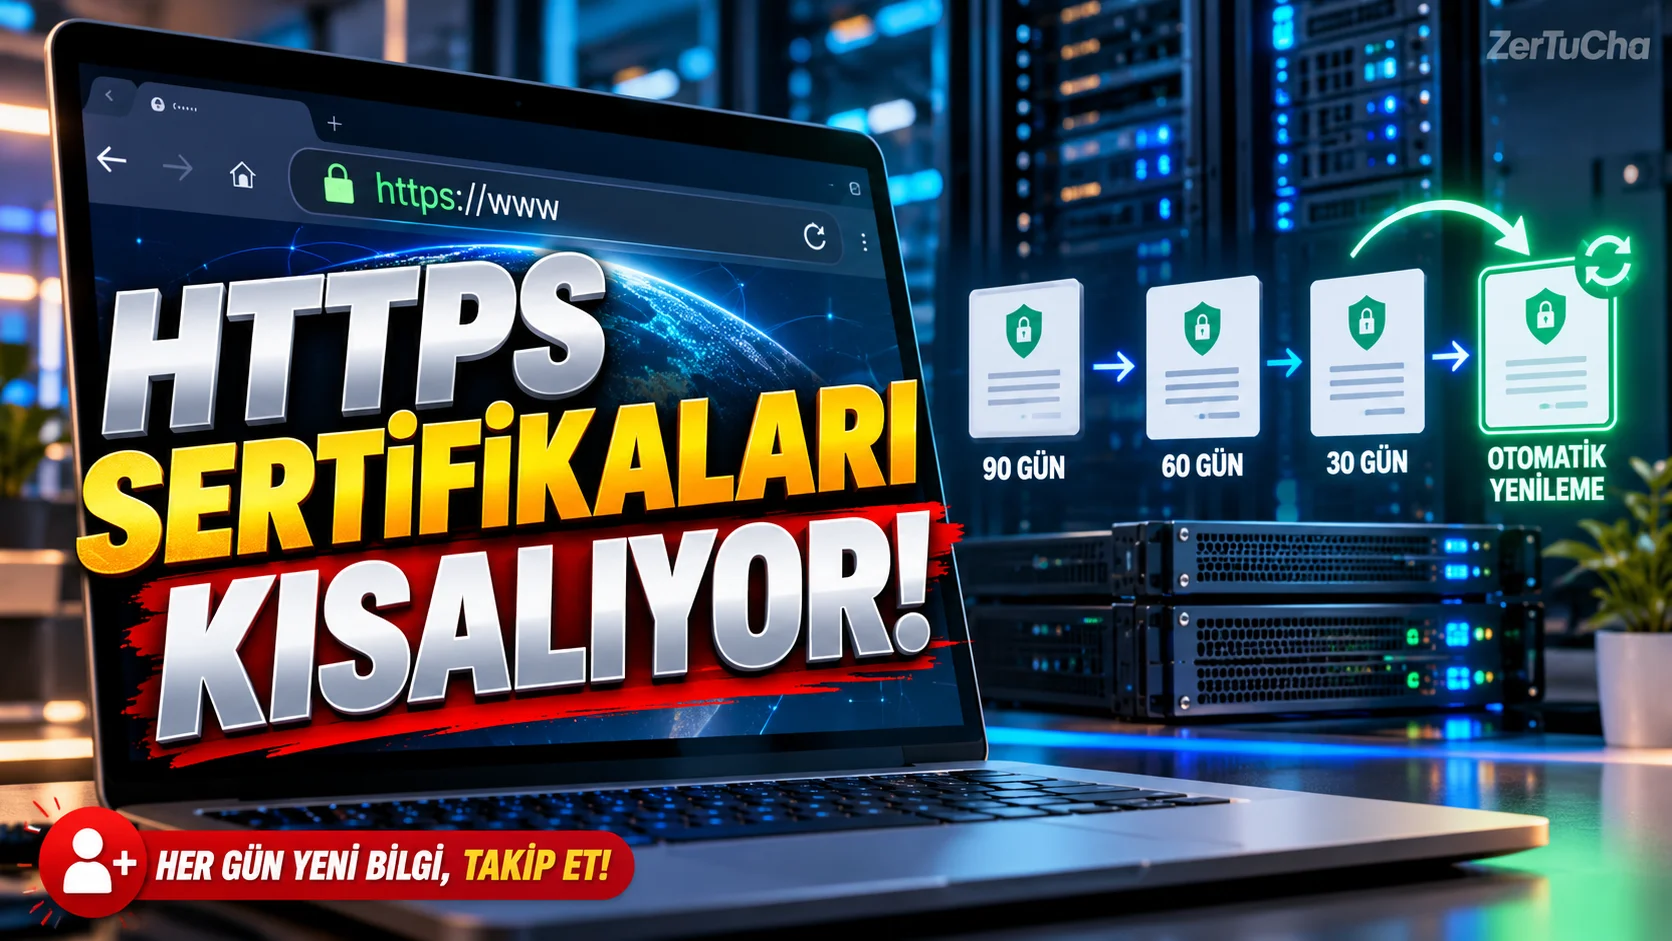
Why is it important to have to renew a website's security certificate several times a year?
When you open a website and see HTTPS in the address bar, it indicates that the TLS infrastructure is used, which helps encrypt the connection between the browser and the server.
In this system, digital certificates help authenticate the domain name. Certificates must be renewed when they expire.
In Ars Technica's news feed dated October 2026, Let's Encrypt's plan to reduce certificate validity periods to 64 days starting from February 2027 is conveyed.
This development is especially important for website owners and system administrators who manage large numbers of domains. Manually renewing certificates can become a difficult task to manage as the number increases.
What changes when the certificate period becomes shorter?
Shorter certificate validity can help reduce the amount of time the risk becomes effective if a certificate or private key is accidentally exposed. However, this does not automatically guarantee security.
On the other hand, when the refresh frequency increases, the operational load also increases. If the certificate renewal process is done manually, a website owner may forget the date and visitors may encounter browser warnings.
That's why automatic certificate renewal mechanisms are important in modern web infrastructures.
How do you check for certificate renewal on your own website?
If you manage a website, the following steps can help you understand your current situation.
-
Find out your certificate provider. Are you using Let's Encrypt or another certificate authority?
-
Determine which tool is running on the server. For example, Certbot or another ACME client may be installed.
-
Check auto-refresh mechanism. Cron, systemd timer, or hosting provider's automation may be used.
-
Run refresh test. Follow the testing method specified in the official documentation of the ACME client you are using.
-
Examine logs. Check if the last refresh attempt was successful.
-
Set alarm. Create a mechanism to receive error notifications before the certificate expires.
-
Add multiple domains to inventory. Verify that not only the main site but also the subdomains have the correct certificate.
The commands here will vary depending on the server and ACME client you are using, so do not assume that a single command is suitable for every system.
Should certification renewal be fully automatic?
Although automation is very useful, just appearing to work is not enough. It should be able to alert when the refresh process fails and the problem should be troubleshootable.
For example, if a domain name fails DNS validation, certificate renewal may fail. Access to the server, DNS records, and permissions of the certificate client should also be checked.
Also, short-term certificates alone will not solve poor server security or a compromised private key. Protecting the private key and keeping the server configuration secure are still essential requirements.
Quick conclusion: Shorter certificate expirations require website owners to set up automatic renewal and monitoring systems more carefully. Instead of managing the certificate only by looking at its expiration date, a safer approach is to test that the renewal mechanism actually works.
Henüz yorum yapılmamış. İlk yorumu siz yapın!
Bir Yorum Bırakın